There’s a microchip in my toothbrush. But WHY? (youtu.be)
WTF Ubuntu? (chalmovsky.com)
The Gift of It's Your Problem Now (2021) (apenwarr.ca)
Jailbreaking my car's navigation system just so I can change the time (blog.nns.ee)
New Release: Tor Browser 16.0 Tor Project (blog.torproject.org)
Virtual Art Museum built with Three js (dostoynikov.bearblog.dev)
eli venn (elivenn.com)
Securing Internet-Critical Software: How We Could Have Backdoored Bash (www.hacktron.ai)
Polyend releases the Tracker firmware source code (backstage.polyend.com)
Recognizing Keystrokes Using WiFi Devices (ieeexplore.ieee.org)
SuperVote: 15 year retrospective on a social endorsement app (callejas.com)

The advantages of mobile Linux over AOSP (amosbbatto.wordpress.com)
gohawk Resource-focused static analysis for Go (gohawk.dev)
Union Types and Option Types (tibleiz.net)
Building a gemini server in python (www.willmunn.xyz)

My reflex of assuming our servers need ever-growing amounts of RAM (utcc.utoronto.ca)
the lost malloc() (napcakes.nekoweb.org)
Tyrtulia, a headless forum with no passwords, made for the terminal (git.andros.dev)
JPEG XS - Wikipedia (en.wikipedia.org)
Optimizing CPU-side Rendering Code (godotengine.org)
A400000 Winners (oeis.org)
The Beginning of BSD Unix (fosscomics.com)
The Problem with C Safety: Modern C Is a Mindset, Not a Standard – MC BLOG (www.modernescpp.com)
Postgres 19 is late, and it's AI's fault (rhaas.blogspot.com)
Understanding Org's LaTeX previews (karthinks.com)
so i guess everyone uses llms to think now (eva.ac)
An easy way to try local AI with braindead-local-intelligence (dataswamp.org)
Work on GEFS (the Good Enough File System) for OpenBSD progresses (www.undeadly.org)

London Meetup - Nov 2026 (lobste.rs)
Spooky C (www.nablag.com)
Let's Encrypt Goes to 64-Day Certificates: When Does Your ACME Client Actually Renew? (devops-daily.com)
Introduction to Programming in ATS (ats-lang.sourceforge.net)
Pratt parsing is a black box (vinipsmaker.github.io)
Zig: From Beginner to Slightly Less Beginner (www.youtube.com)
A Specialised Haskell Processor on FPGA (bathtub-01.github.io)

Dead Internet theory (en.wikipedia.org)
An outsider's perspective on Scion and Mononoke (typesanitizer.com)
groff/troff macros: ms, mm, me or mom (www.stephenlindholm.com)
Beating the compiler at signed 32-bit division (lemire.me)
Release 0.6.0 · buzz-language/buzz (buzz-lang.dev)
No AI, 52 min. Build all Linux Files utils in C by Hand (www.youtube.com)
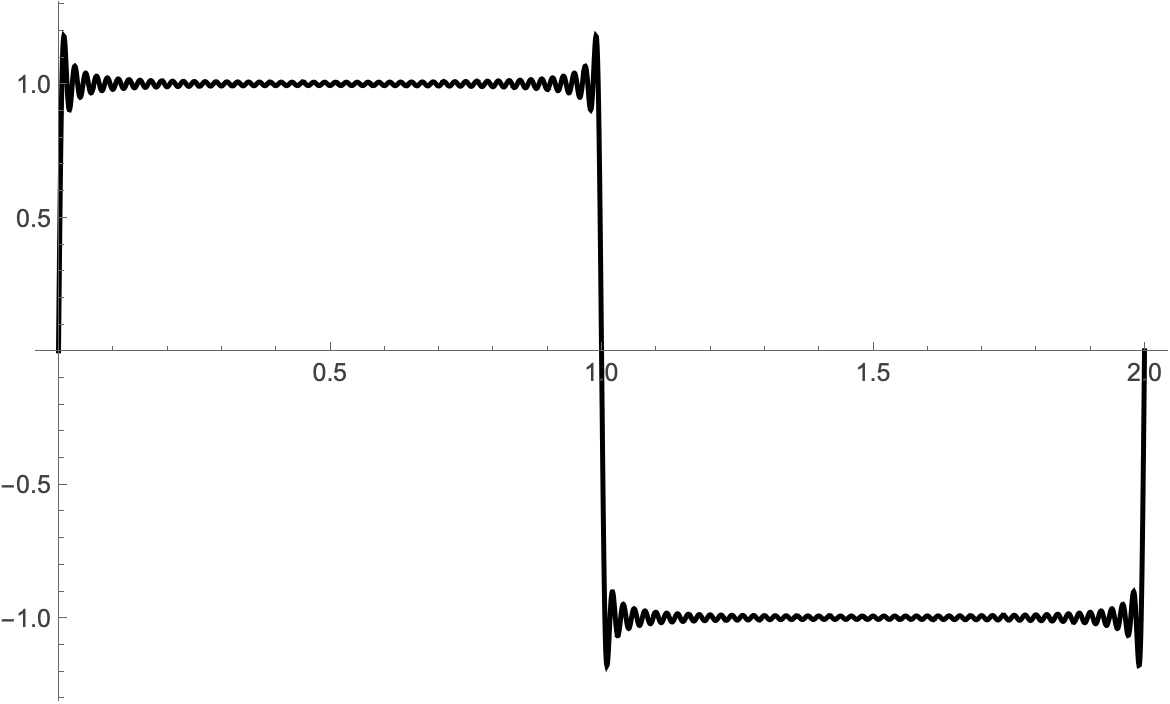
XKCD and Fourier (leancrew.com)
Non-Determinism and Overcount on Modern Hardware Performance Counter Implementations (web.eece.maine.edu)
A brief history of just-in-time (2003) (dl.acm.org)
Introducing Kwi, a new KDE terminal emulator (blogs.kde.org)
The Duty of a Scholar (www.daemonology.net)
Effective Type: Part 1 (uecker.codeberg.page)
Novellas with groff (movq.de)
A game scripting language that runs speech-to-text 5x faster than llama.cpp on CPU (dasllama.io)
Mystery of 60-Second Fluctuations in Power Grids Solved (www.fz-juelich.de)
Avoid Public Functions Calling Other Public Functions (matklad.github.io)
Enlightenment 0.28.0 Release (www.enlightenment.org)
Speeding up GPU copies by permuting iteration spaces, or, optimising the identity function (futhark-lang.org)

Tangled, hire a front-end accessibility expert (dbushell.com)
An LC-3 Disassembler in Haskell (abhinavsarkar.net)
CVE-2026-116155: ImageMagick Memory Leak via Crafted XMP Profile (www.agilehunt.com)
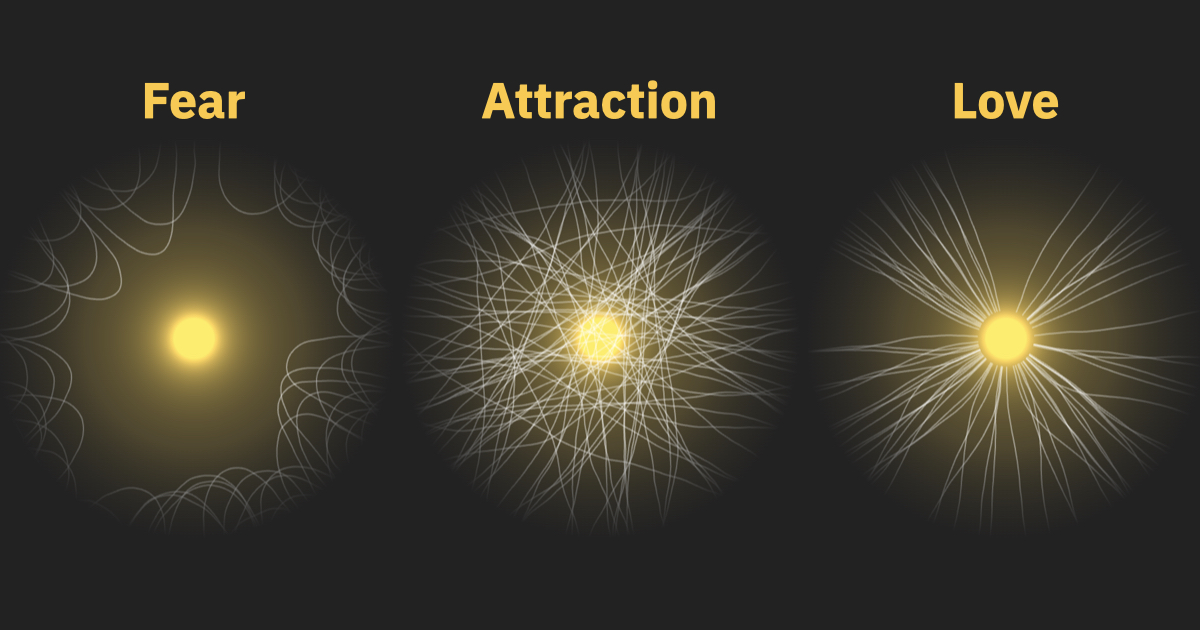
Let’s Build a Brain (aatishb.com)
The Kluever Maneuver (jordi.inversethought.com)
We Won’t “Just Hang Out” (borretti.me)
Jepsen: ParticleDB 1.1.4 (jepsen.io)
Digital minimalism (vitalik.eth.limo)
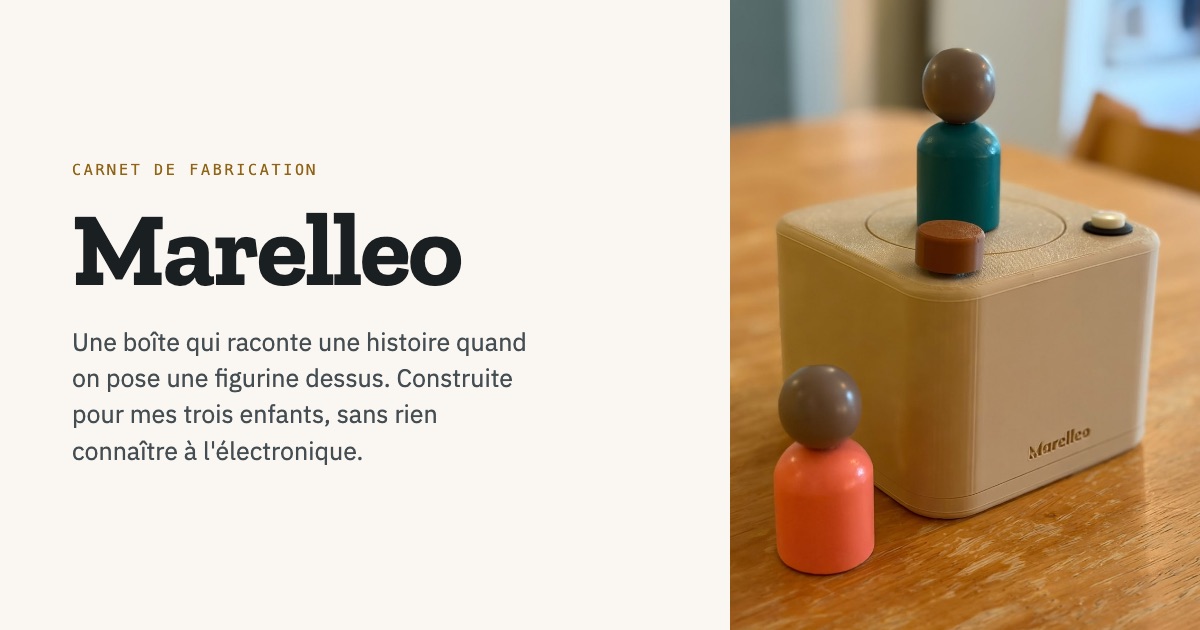
Marelleo, a story box I built for my kids (zebra.rodeo)

The Secret of Fast Programming: Stop Thinking » (www.codesimplicity.com)
Clojure/Conj 2026 (www.youtube.com)
Tactical-Retreat: a freely available, multi-platform QuakeC-based Counter-Strike v1.5 port (www.frag-net.com)
The top ten reasons embedded projects get into trouble (2002) (www.ganssle.com)
The support case of a customer who said that all they could see was a black screen (devblogs.microsoft.com)
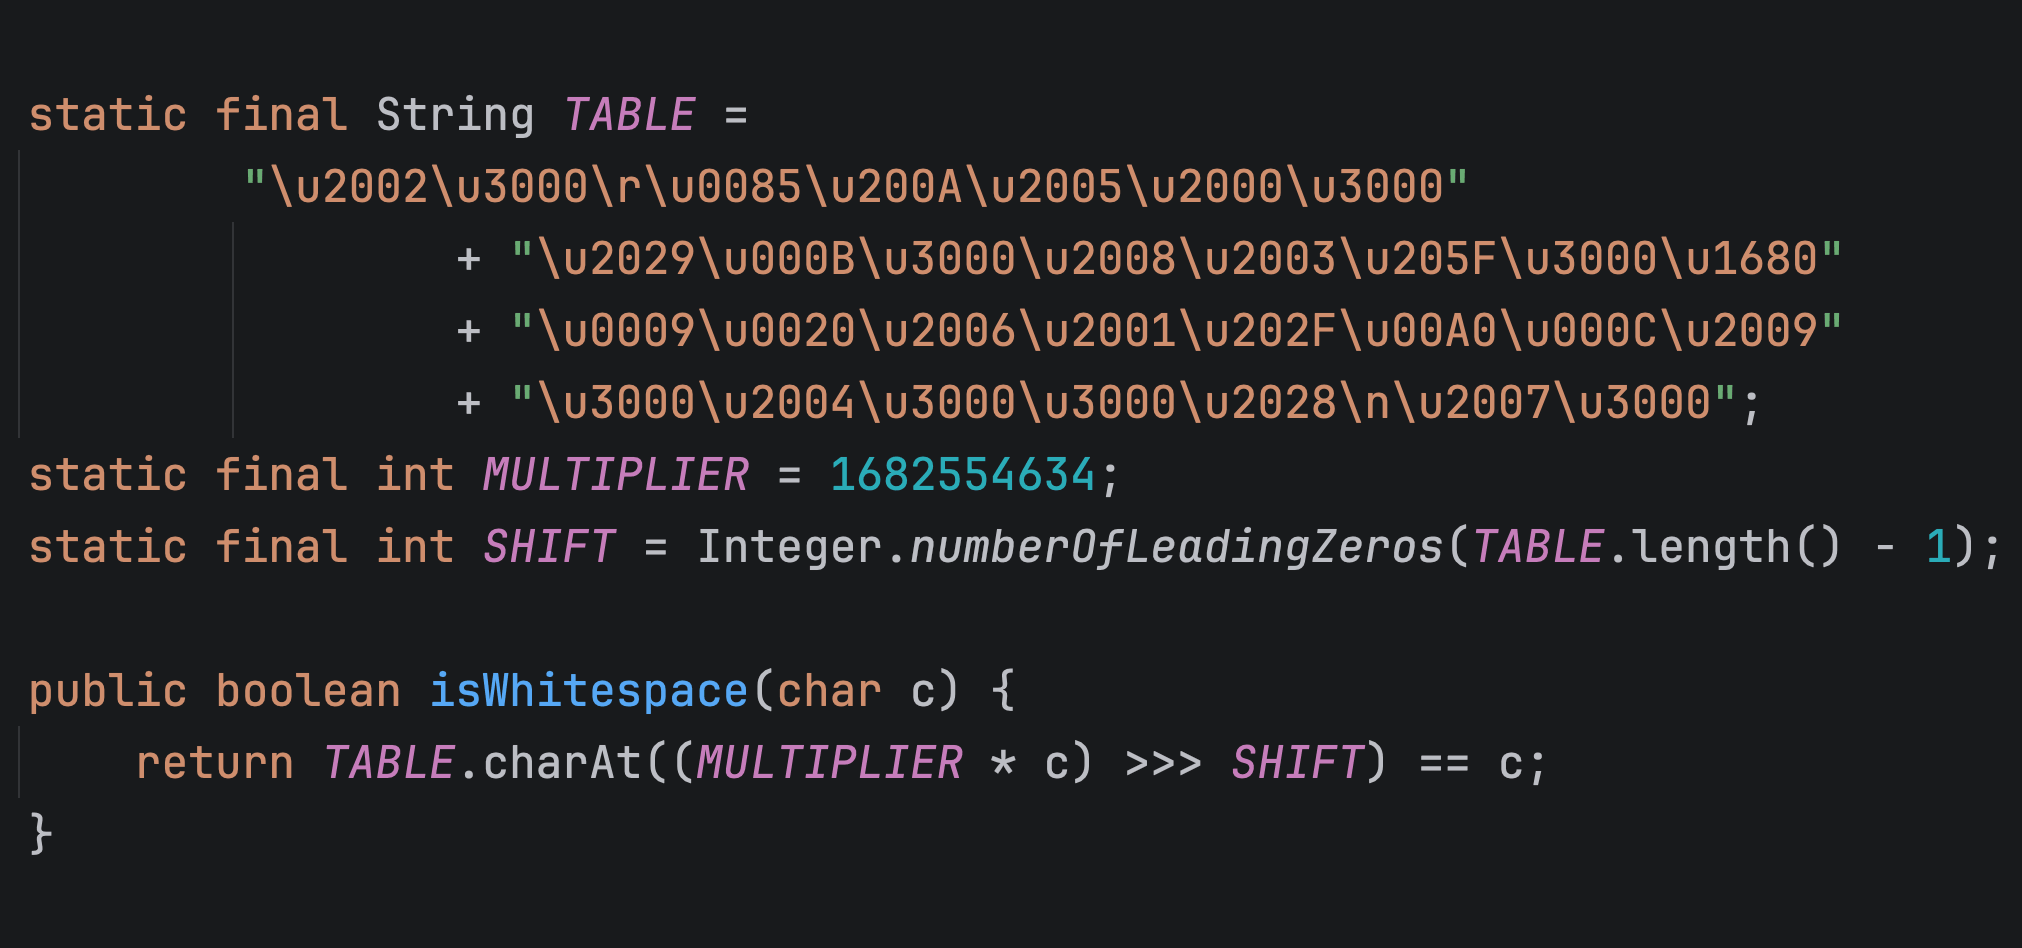
How hard is it to check for whitespace? (serce.me)
Defending the patch gap against automated attackers (blog.mozilla.org)
Why Antithesis? (antithesis.com)
Getting Google Cast on my Soundbar (codon.org.uk)
Switch lowering in GCC (xoranth.net)

Linux Kernel TCP Flaw With 9.8 CVSS Score Affects Ubuntu, Red Hat and Other Distributions (thehackernews.com)
Protecting against CVE-2026-98432 (groups.google.com)
The federated code forge (tangled.org)
Rationale for filtering LLM usage links as off-topic (lobste.rs)
Building fine-grained version control for agents with Rust and Durable Objects (delta.dev)
Infinite Mac: BeOS (blog.persistent.info)
Go 1.28's HTTP/2 Parking: Measuring Memory Savings (abdolirad.me)

Shrinking NixOS Ram footprint and resource requirements to the bare minimum (lowendspirit.com)
No, npm, “estee” is not a typo of “testem” (smoores.dev)
Update on AO3 Downtime, October 30, 2026 Organization for Transformative Works (www.transformativeworks.org)
Anthropic hacked to deliver remote access trojan to Claude developer laptops worldwide (doublepulsar.com)
Smart audio for the smart home (2021) (computer.rip)
Do At-Proto Users Know This Is Public? (melaniekat.com)
Backdoors in Claude Code for VS, Cursor official extensions (cyberplace.social)
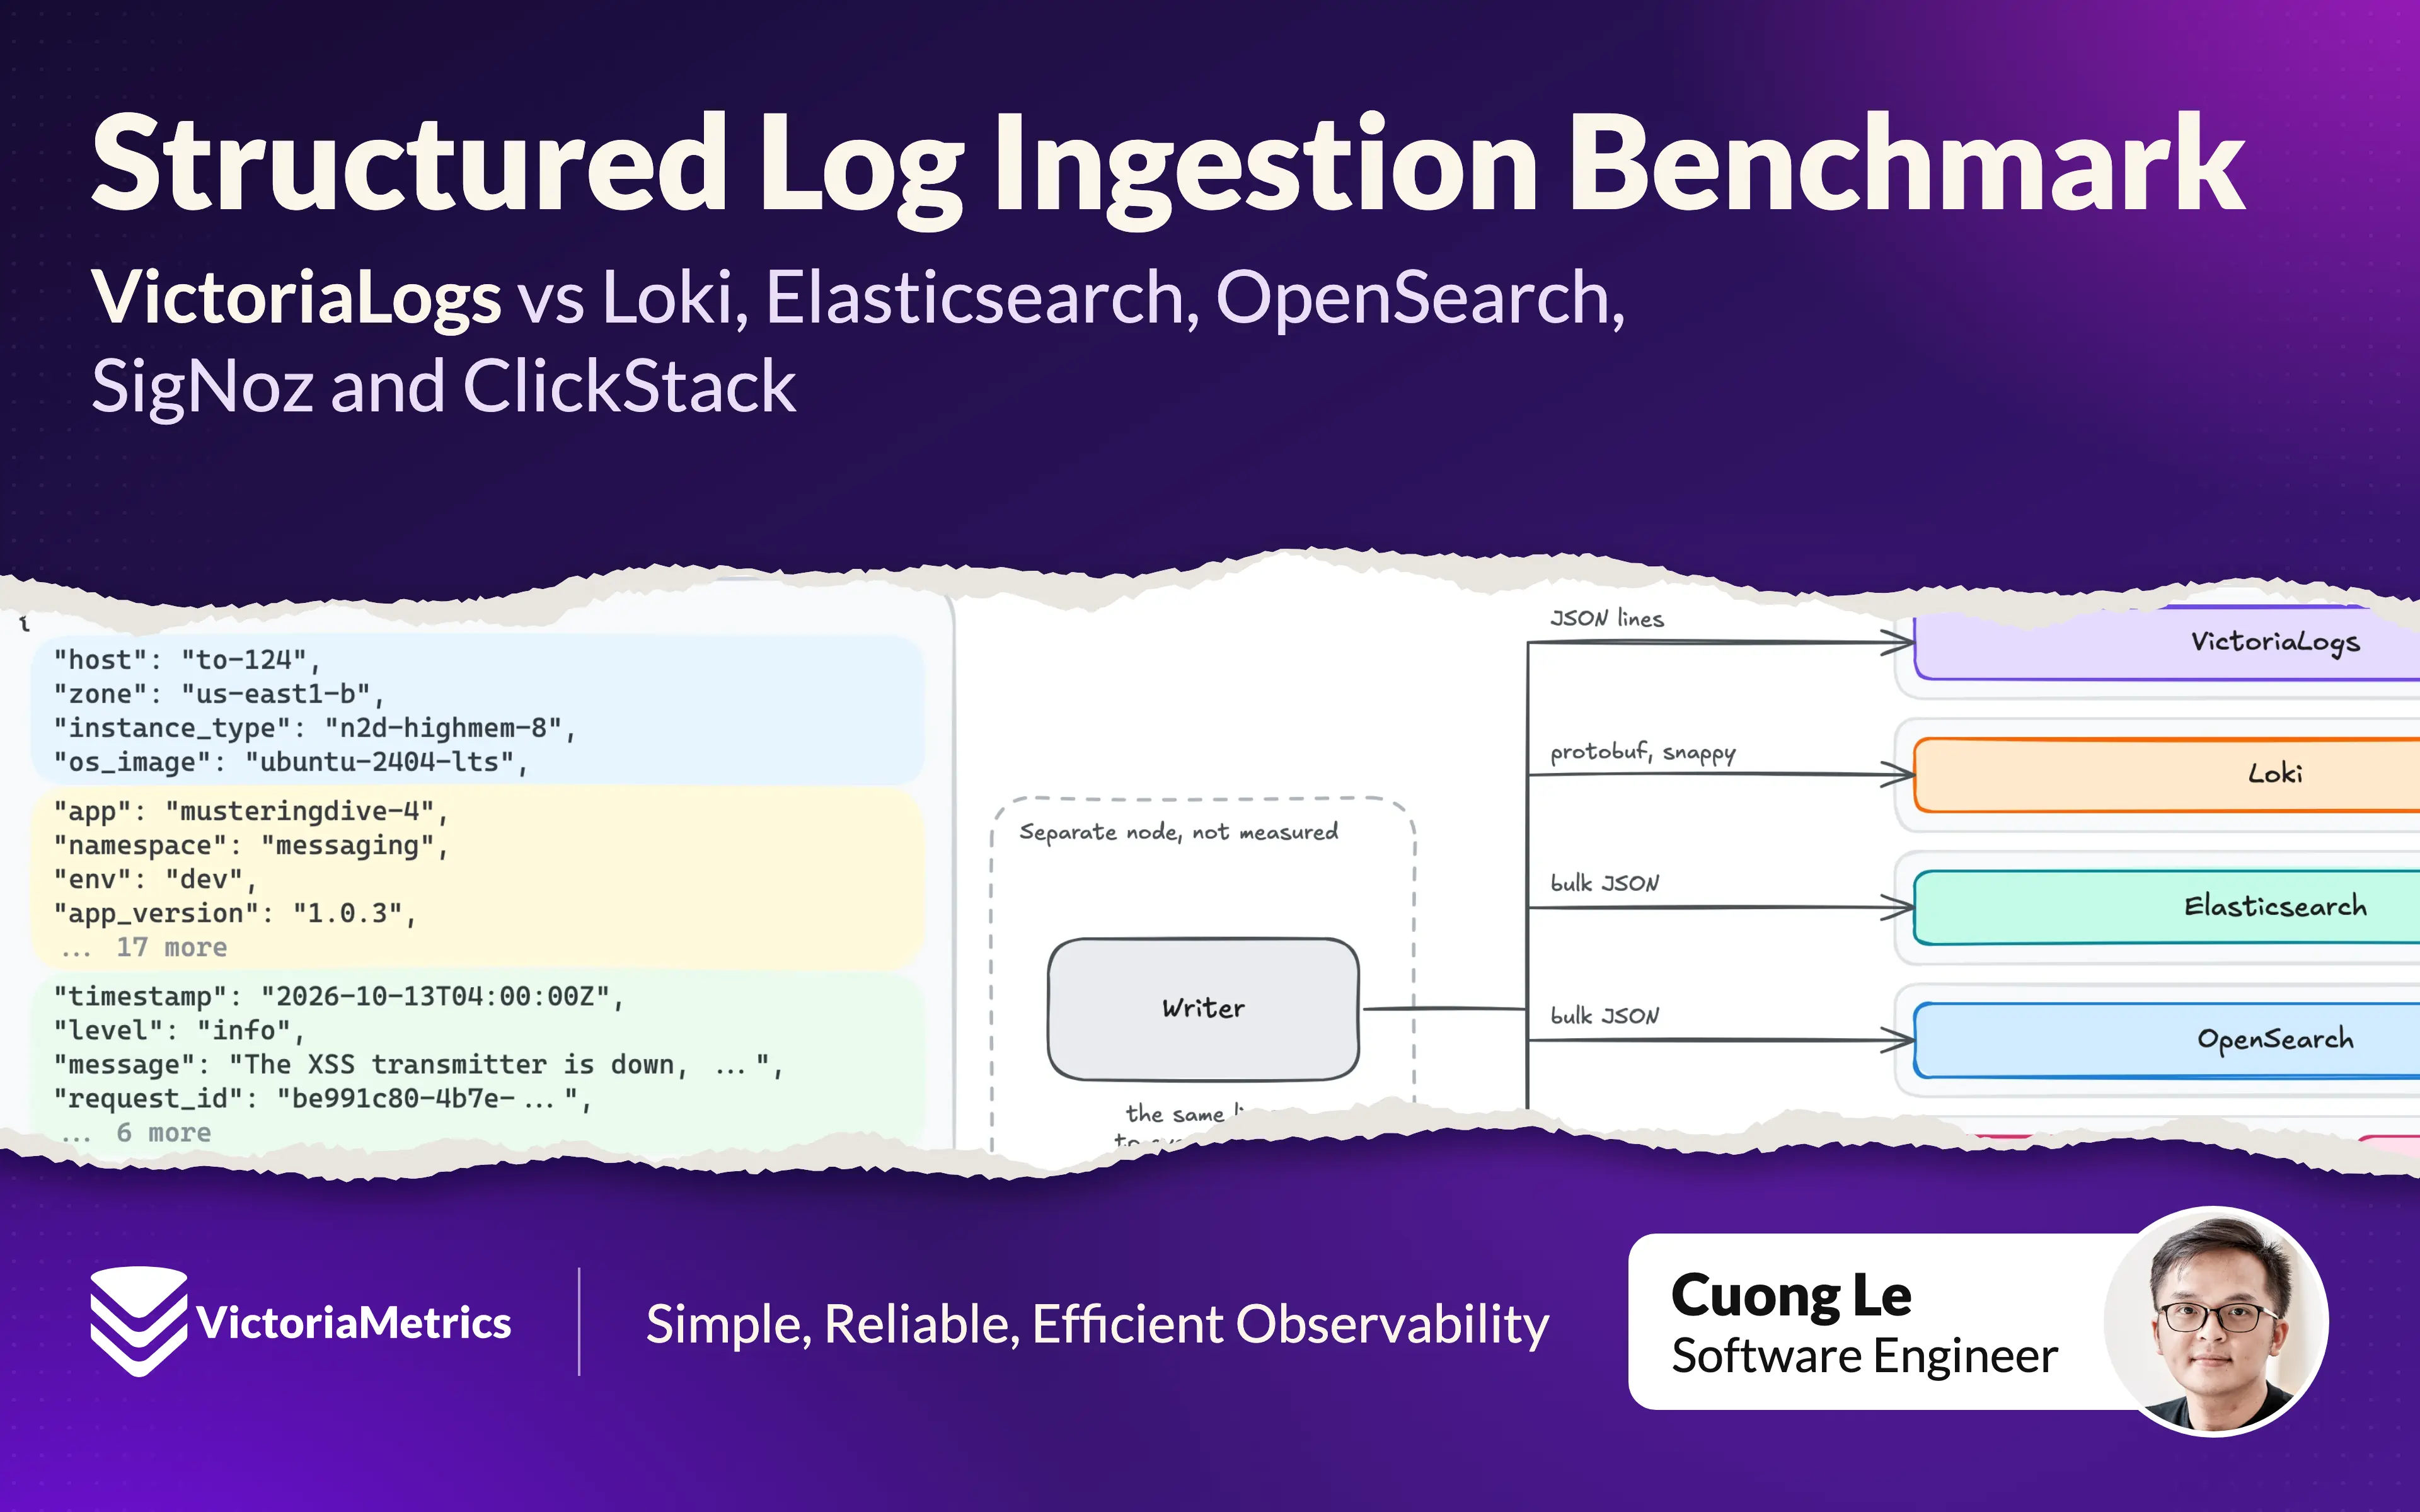
VictoriaLogs vs Loki, Elasticsearch, OpenSearch, SigNoz and ClickStack on structured log ingestion (victoriametrics.com)

arm64e pointer authentication: PAC keys, PACIASP, A12 (sigreturn.com)
How curl was accidentally Turing-complete for nine months (seriot.ch)
ztmux the pure Rust tmux superset (github.com)

Pidgin 3.0 Alpha 4 2.98.0 has been released (discourse.imfreedom.org)
gh-inbox: clean up GitHub notifications in bulk from the command line (github.com)
If you love a website, back it up (blog.mistys-internet.website)
Design the interface for functionality not familiarity (lapcatsoftware.com)
XSS in yarr RSS reader (0x67673068.me)
C2PA's eMudhra Moment (www.da.vidbuchanan.co.uk)
Cybersecurity Is About to Be the Biggest Problem in Tech (projectautonomy.substack.com)
noalloc: Tooling and libraries to enforce zero heap allocations in Golang (github.com)

Will Open Firmware Become the Next Big Trend in Electronic Music Gear? (www.synthtopia.com)
My favourite PowerMac is a Nintendo Wii (virtuallyfun.com)
Extremely brief history of PDP computers (entropicthoughts.com)
An open format for writing agent-native software requirements (slcr.dev)
Phorge (www.phorge.it)
Coding Agents, Starter Kits and pgledger (www.pgrs.net)
The Web Can't Afford a JavaScript Runtime Monoculture (redmonk.com)
Azure’s Weakest Link - Five Full Cross-Tenant Compromises (www.binarysecurity.no)
Shared password manager for families? (lobste.rs)
Building NixOS using Nixtamal (nixtamal.toast.al)
"You Already Don't Understand Your Code": What "ten sorts in ten languages" and various JS engines say about the abstraction we're living through now (george.mand.is)
Nim version 2.4.0 released (nim-lang.org)
NetBSD adds a new beginner-friendly text editor called atto (mastodon.sdf.org)
Syrinx: A censorship-resistant communications platform (var0xyz.github.io)
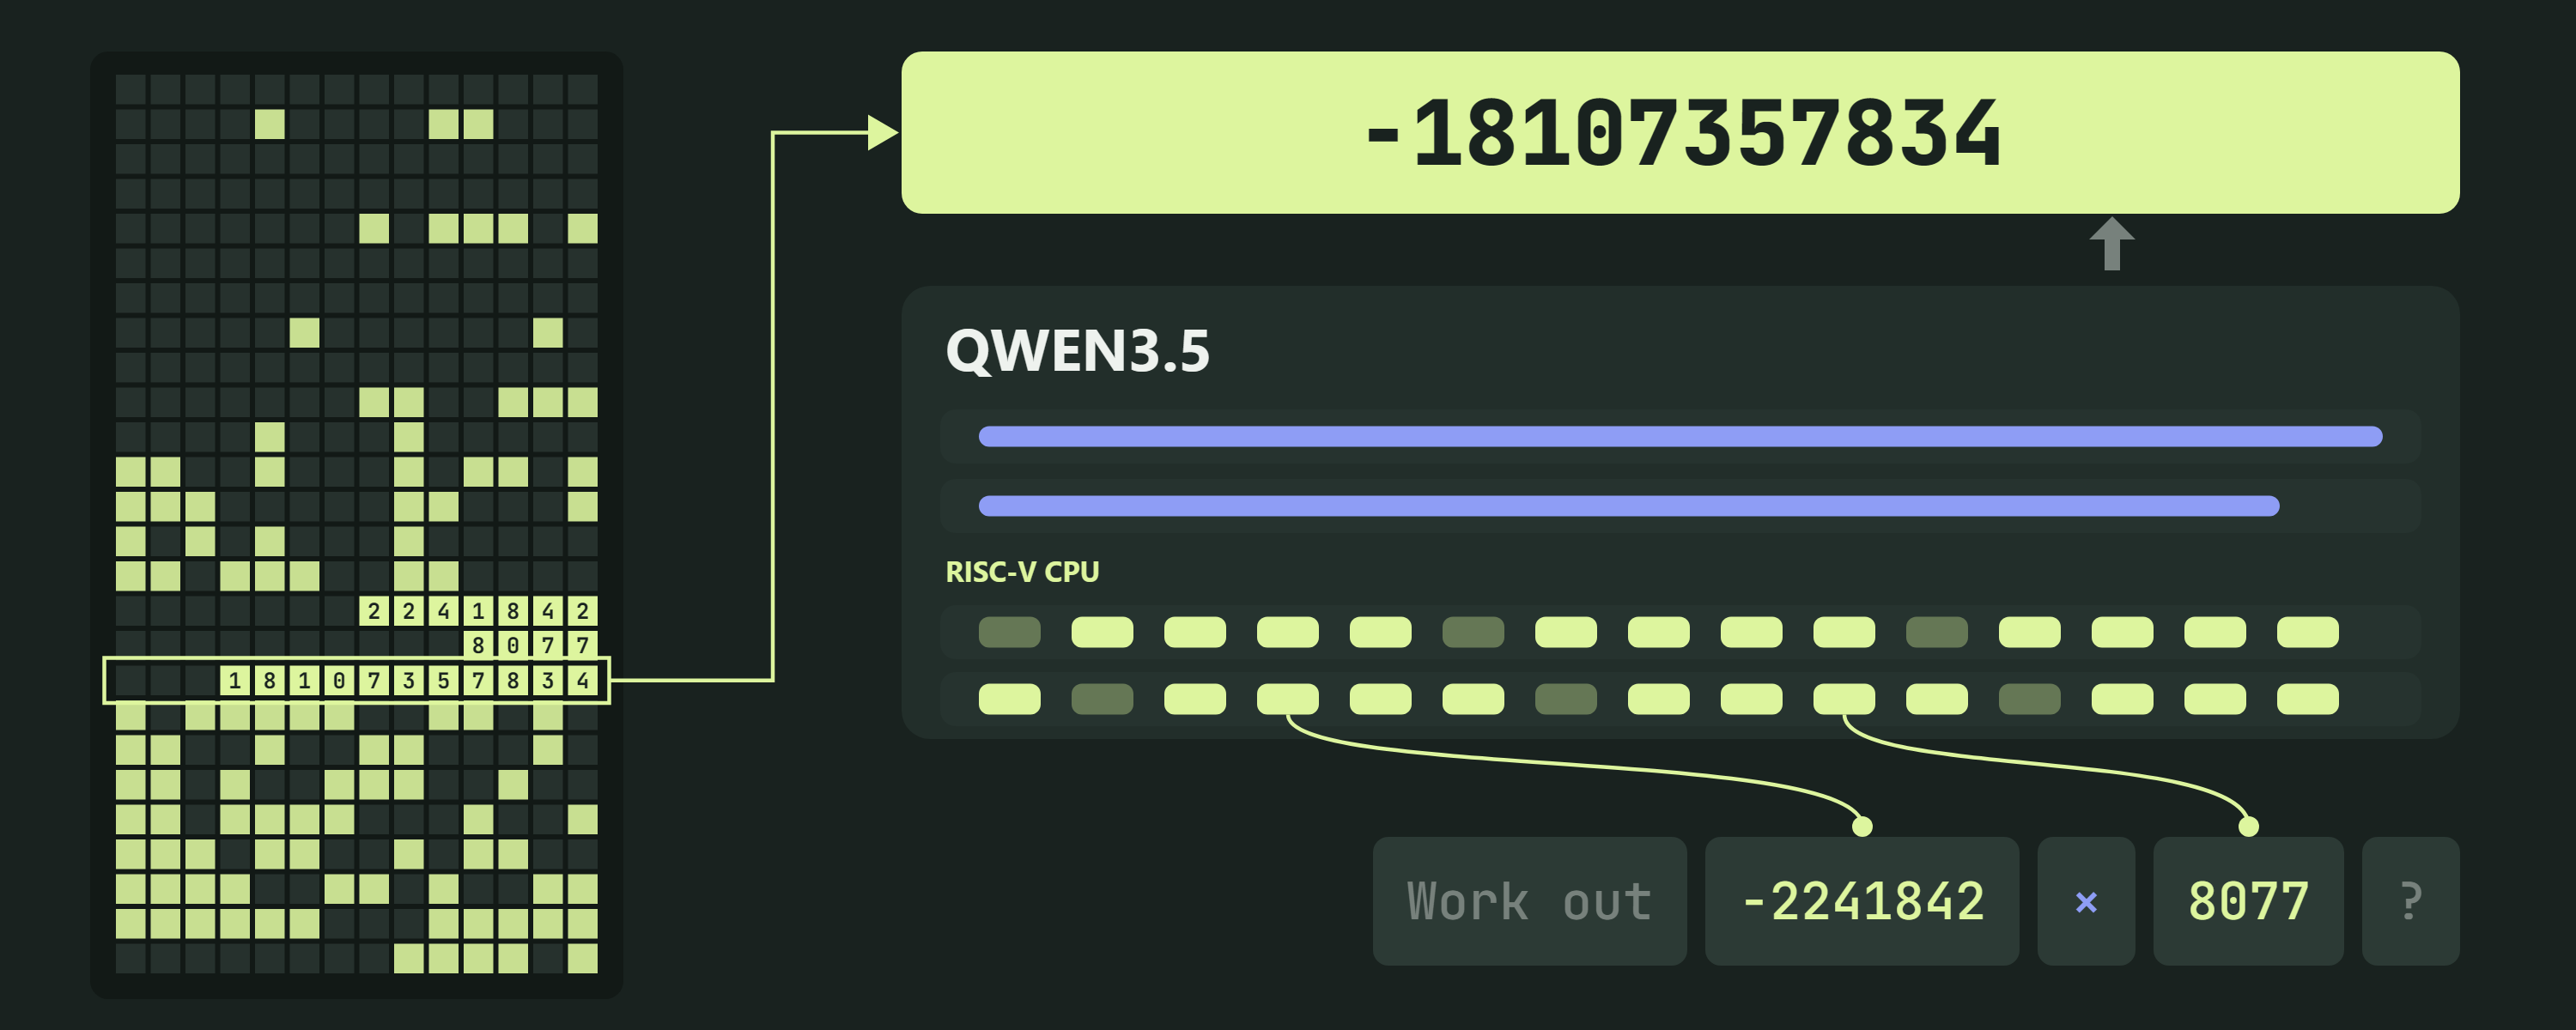
Qwenputer: a fully functioning, deterministic RISC-V CPU inside Qwen3.5 (divagr.com)
Go Empty Interface Explained & The Hidden Heap Allocation (www.youtube.com)
My Terminal Setup in 2026: Ghostty, tmux, and Neovim (nick-liu.com)
A single malformed WAP Push SMS crashes com.android.phone on Android, dropping active calls (including emergency calls) (smsofdeath.com)
What the fox say? (entropicthoughts.com)
Uji - Gentoo of Coding Agents (github.com)
The Future Trait Has A Missing State (blog.yoshuawuyts.com)
ACLs don’t (2009) (shiftleft.com)
The case of the 9 bit AES key (v12.sh)
Redox Ring Buffers Project Summary (www.redox-os.org)
I've never been a fan of these calculators (www.youtube.com)
Precedence levels are dead; long live precedence sets (www.corsix.org)
Cuis Smalltalk (cuis.st)
Why I still teach OpenGL ES 3.0 (eliasfarhan.ch)
Introducing the Accessible Components Library (tetralogical.com)

EMACS turns 50 (www.technologyreview.com)
GitLab security incident: attempted exploitation of CVE-2026-97229 Alpine Linux (alpinelinux.org)
Why Is This Fingerprinting Script Creating Bioweapons? (nullpt.rs)
Foundational Cryptography in SPARK (www.adacore.com)
OpenBSD Jumpstart 8.0: Quick Start Guide for New Users (openbsdjumpstart.org)
Hoot 0.10.0 released (spritely.institute)
Pair-coding Lobste.rs feat (lobste.rs)
GOTO Considered Totally Sick (for error handling in C) (thestateofinahaze.net)
Making SIMD Code Scale to Any Vector Width (streamhpc.com)
Raspberry Pi Zero 3 W and Pi 4 Model A on the Way? (bret.dk)

The October inflection point for vibe game development (simonwillison.net)
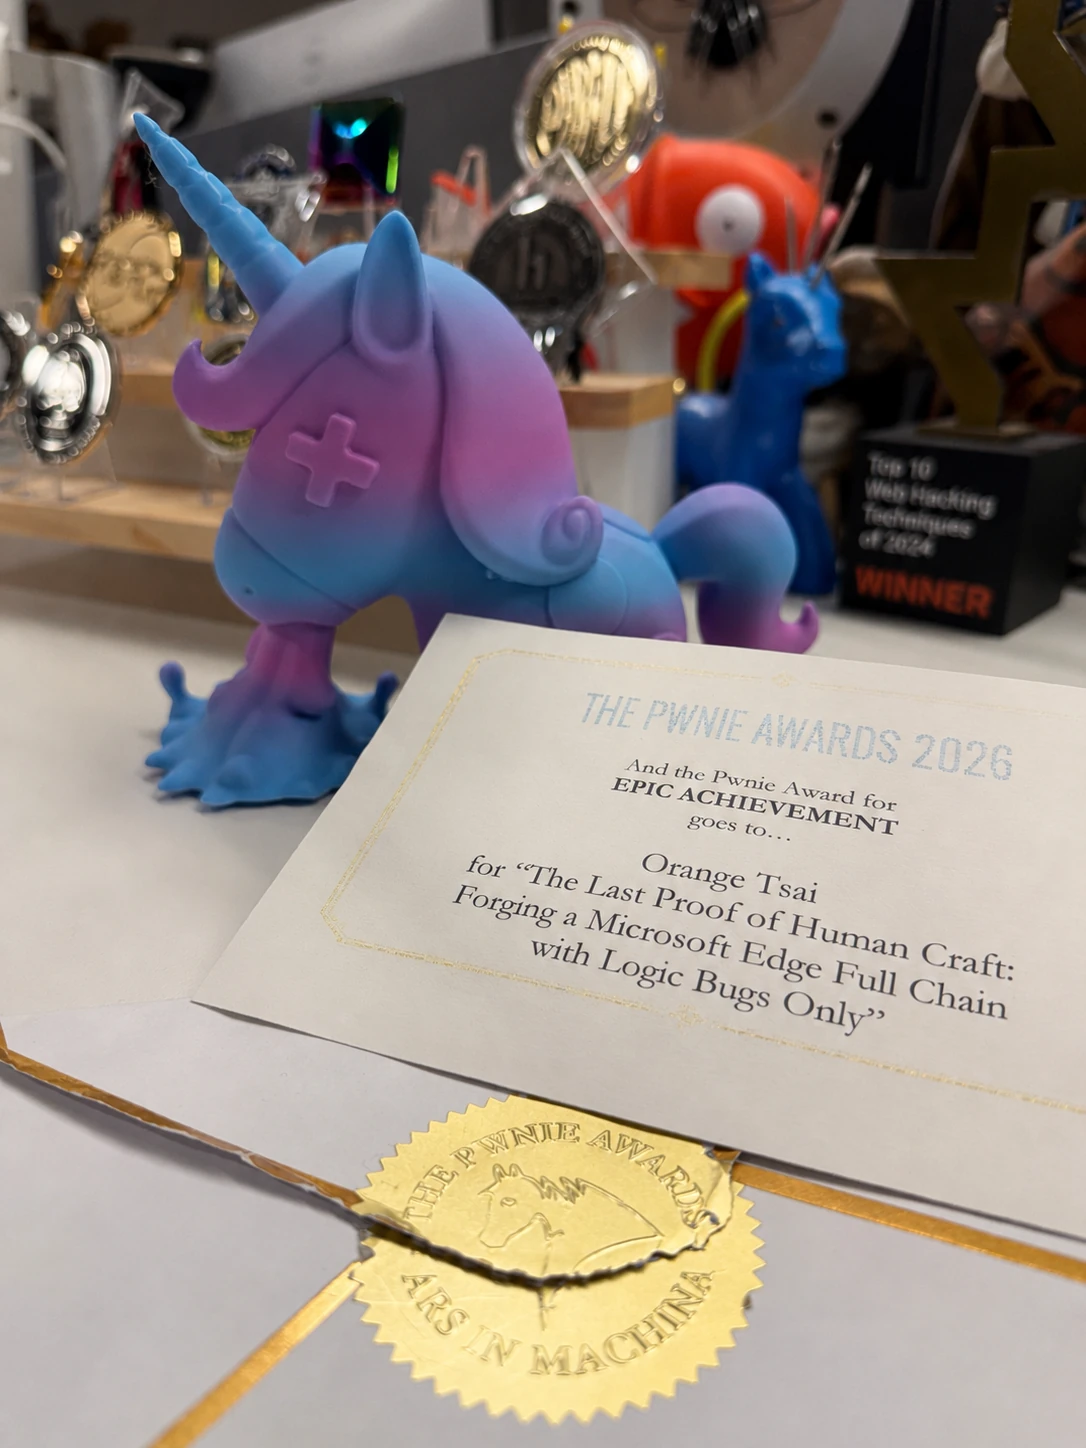
Forging a Microsoft Edge Full Chain with Logic Bugs Only (blog.orange.tw)
Apple's git still trusts the compromised eMudhra certificates (emudhra.we-have-a-problem.com)
A Little Bit of Slope Makes Up For a Lot of Y-Intercept (www.youtube.com)
AlpineBSD (wiki.alpinebsd.org)
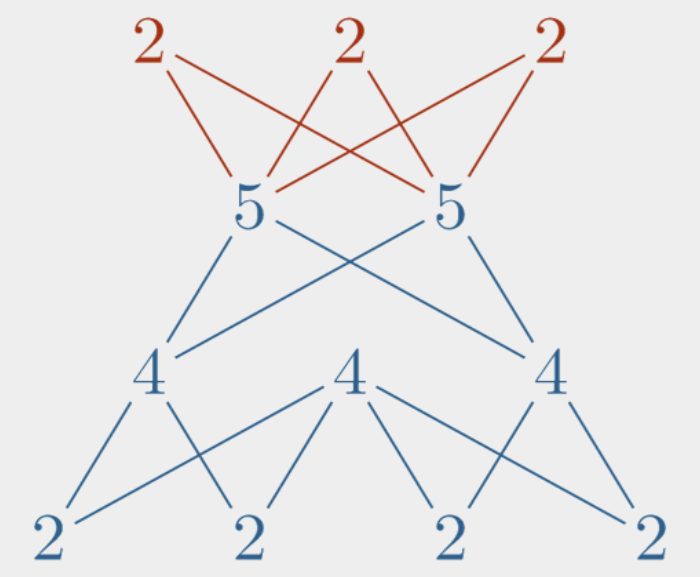
Start Doing Graph Theory (vertex.degree)
Hunger beats tenure: Advice for junior engineers (felixrieseberg.com)
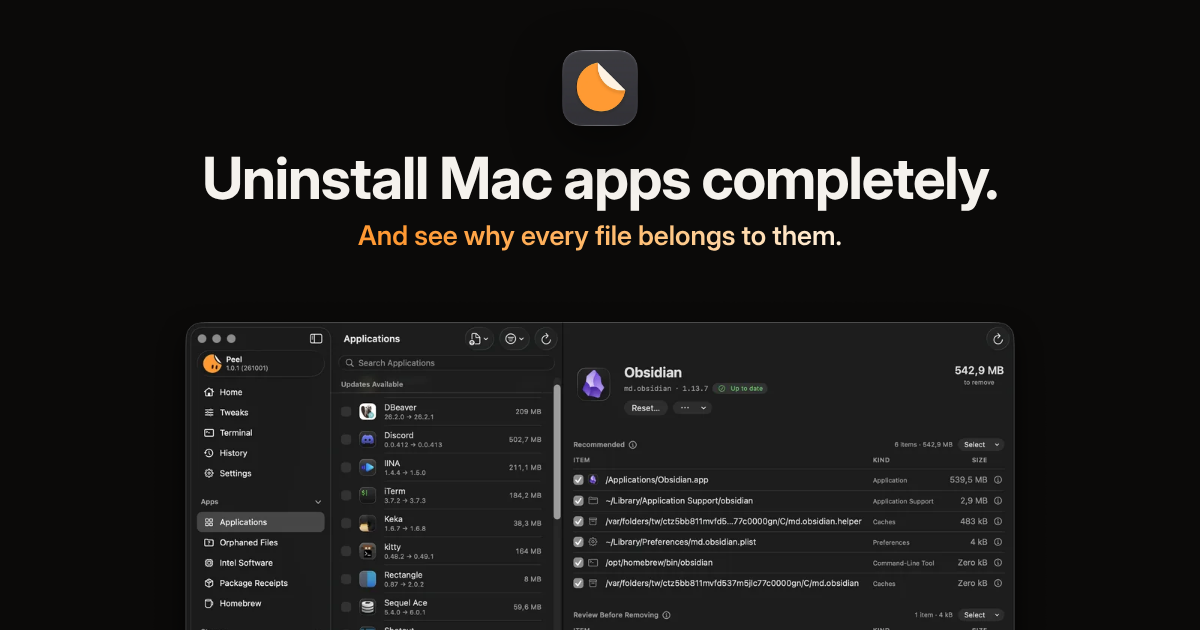
Peel: A free, open source uninstaller and cleaner for macOS (peel.tuguidragos.com)
Billion-query-per-second lookup tables in C (lemire.me)
Code-execution flaw in UEFI firmware affects most servers on planet Earth (arstechnica.com)
The Benchmarking Crisis (databasearchitects.blogspot.com)
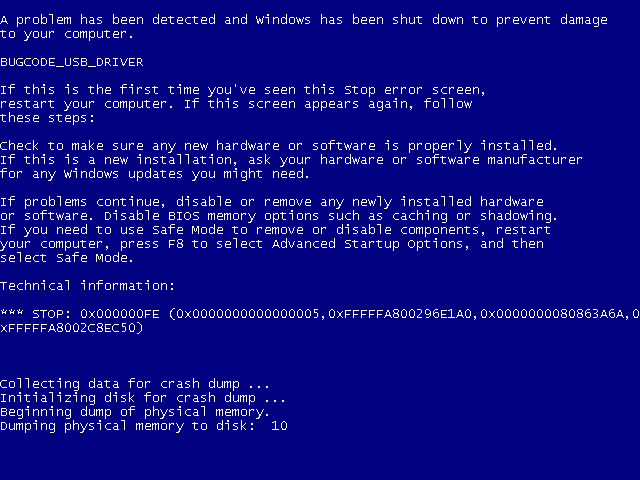
Who’s 0xabadbabe and why? (2011) (daniel.haxx.se)
Scalable Vector Grief (portswigger.net)

Git for the US Code (lexifina.com)

This is not sustainable (www.netmeister.org)
Reminder: Lobsters NYC Meetup Tomorrow 5:30 at Walker's (lobste.rs)
Coders’ Rights Project Reverse Engineering FAQ (2017) (www.eff.org)
Tailscale SSH: Investigation and remediation update (tailscale.com)
Ghostty 1.4.0 (ghostty.org)
Fixing KIO copy to USB stick and network filesystems (blogs.kde.org)
The next circle of security hell (blogs.gentoo.org)
An Evening with Berferd: In Which a Cracker is Lured, Endured, and Studied (1992) (www.cheswick.com)
Fuzzers vs. AI: Comparing Fuzzilli and BigSleep on JavaScript Engines (projectzero.google)
Four Months of Zig (gracefulliberty.com)

1,447 emoji? We'll do it live (planetpeanut.studio)
Protobuf in Python and TypeScript is actually good now (buf.build)
The Shift of Theseus — Toy Bit Provenance Abstract Domain (www.pypy.org)
A fast and secure tar parser for the Rust ecosystem (astral.sh)
Finding panics with Call Graph Analyzer (tweedegolf.nl)
Filian, Fil-C binaries on Debian (cr.yp.to)
A stackless floodfill automation (2023) (t3x.org)
Compile-Time Dependent Types (thenumb.at)
slughorn — GPU Vector Graphics (slughorn.io)
EnsoJS - native-first microframework for building declarative Web Components (ensojs.dev)
Gforth 1.0 (gforth.org)
A select should tell you something (alfy.blog)
Full Haskell-like Type Class resolution in Java (garciat.com)
TypeScript and Haskell: Unions & Singletons (2024) (garciat.com)
Code.org's Excellent Beginner Programming Courses Gets Lost in the AI Hype (studio.code.org)
Keyless Entry: Hacking SwitchBot Smart Locks (neodyme.io)
Python's experimental JIT to be removed (lwn.net)
Our Response To The eMudhra Key Disclosure Incident (go.dev)
The Exponential Time Hypothesis Is False [pdf] (github.com)
(VCF Midwest 2026) Building a Living 90s Internet for Vintage Computers (www.youtube.com)
The passkey is worse (www.kcoleman.me)
Shitty Screenshare (shittyscreenshare.com)
MEU - a M3U file editor (github.com)
The Limits of Fingerprint Blocklists: A Reproducible Java Certificate Bypass (www.sonatype.com)
Oldest GUI application that still runs on Windows 11 (blog.enlyth.com)
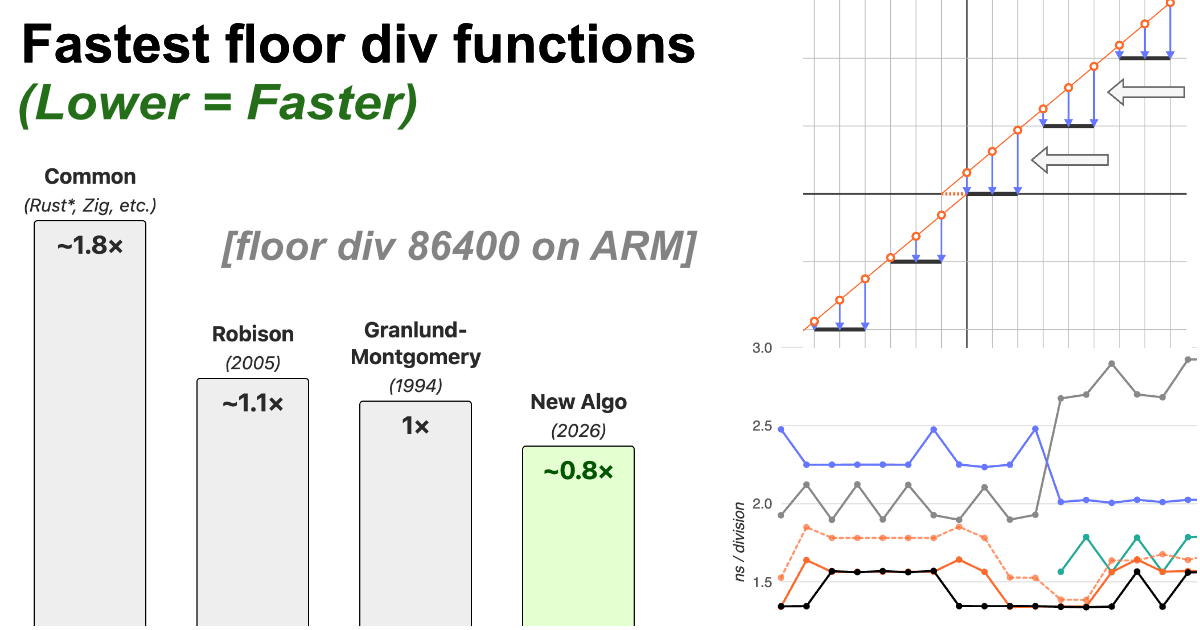
A faster way to compute signed 64-bit floor division by constants (www.benjoffe.com)
CSS-Tricks has a new owner (css-tricks.com)

The result of the C26 DIS ballot (train-it.eu)
Pharo 14 Released (pharo.org)
Web Page Crawler Revealed - tracking down requests from Contabo GmbH (bruceediger.com)
Stalwart v1.0: The Fastest Mail Server on the Planet (stalw.art)
Heavenly delights of hashing numbers under EQUALP (turtleware.eu)
Simple Sudoku Solver in Assembly (blog.veitheller.de)
Why is it so expensive to send an email? (evancz.dev)
Shadow: Dummy folders, an obvious overflow, and a ROP chain (chirp.tene7.com)

Aggro is the Foundation (2022) (radimentary.wordpress.com)
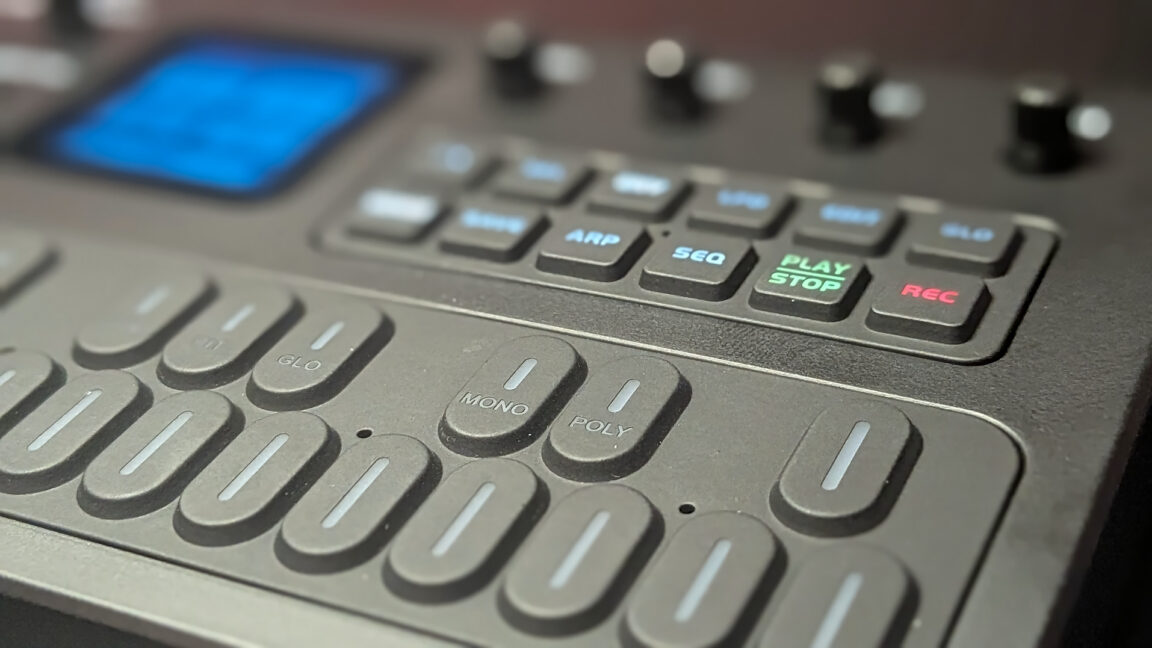
From impulse purchase to pocket studio: The M-Vave FM-1 (arstechnica.com)
Websites Should Be Printable (brennenputh.me)
Gram 3.4.0 released (gram-editor.com)
What are you doing this week? (lobste.rs)
The Small Web is Huge (dn711504.ca.archive.org)
Wails v3.0.0 Released (v3.wails.io)
Akku.scm 1.2.0 released (weinholt.se)
MoLE Protocols (datatracker.ietf.org)
About the compromised eMudhra intermediate CAs (support.apple.com)
OpenLDK: Bringing the Java World into Common Lisp (atgreen.github.io)
The State of Context Engineering (www.dbreunig.com)
writing about pratt parsing so I remember it (www.unix.dog)
“AI Skills” are worthless in 2026 (fishbowl.pastiche.org)
Simple NetBSD webserver (bsandro.tech)
Two musings on the design of compiler warnings (2020) (quuxplusone.github.io)
Reverse-Engineering Instruction Encodings (2001) (www.usenix.org)

Building Java ME Apps with Modern Tooling (voxelmanip.se)
Every Clojure Talk Ever (www.youtube.com)
When a glibc update accidentally breaks Chromium's audio (2021) (refi64.dev)
POSIX wordexp(3) is dangerous (yossarian.net)
Vim Classic (vim-classic.org)

A vision for a next-generation timeline (media.ccc.de)
SIMD-accelerated computer vision on a 2 microcontroller (shraiwi.com)
Partial Order Precedence (ziglang.org)
Reflections on DeepSeek Open-Sourcing Its Inference Engine, DeepInfer (wukong123.substack.com)

The Slurptop: A home-built luggable that runs on power tool batteries (slurpburgers.com)

The Tool Book of a Nuremberg Knight from 1505 (loeffelholz-codex.org)
Steal My Bitcoin (stealmybitcoin.com)
Decompiling Fast Food Tycoon 2 (healeycodes.com)
Michal Wallace on Narrative Programming (alexalejandre.com)

Nim vs Rust: Language is a Matter of 'Coherence', Not 'Performance' (wintrover.github.io)

MacOS Extensions pack for the Apple Network Server v1.0 (oldvcr.blogspot.com)

Scrawl: show an agent the problem (scrawl.kitlangton.com)

SIMD and Go (internals-for-interns.com)
We should be more ambitious with the software we build (danluu.com)

Balloting has completed for C26. Unfortunately it was Disapproved/ (www.linkedin.com)
The Polyglot's Dilemma: Conformance Testing a Dozen Specs in as Many Languages (emptysqua.re)
2026 Ruby on Rails Community Survey Results (railsdeveloper.com)
enzyme: Local-first compile step for knowledge bases. Save 350x cost, 1000x speed vs. frontier models (github.com)
Bringing uv and ty together (astral.sh)
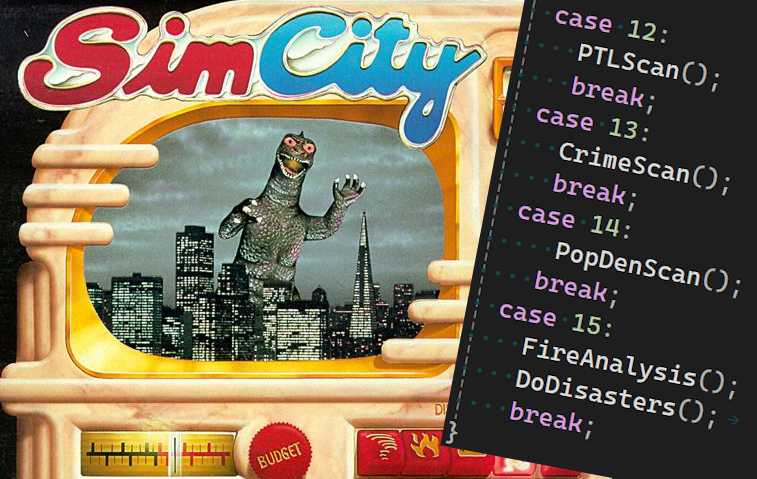
How to run a city builder on 16 MHz (larstofus.com)
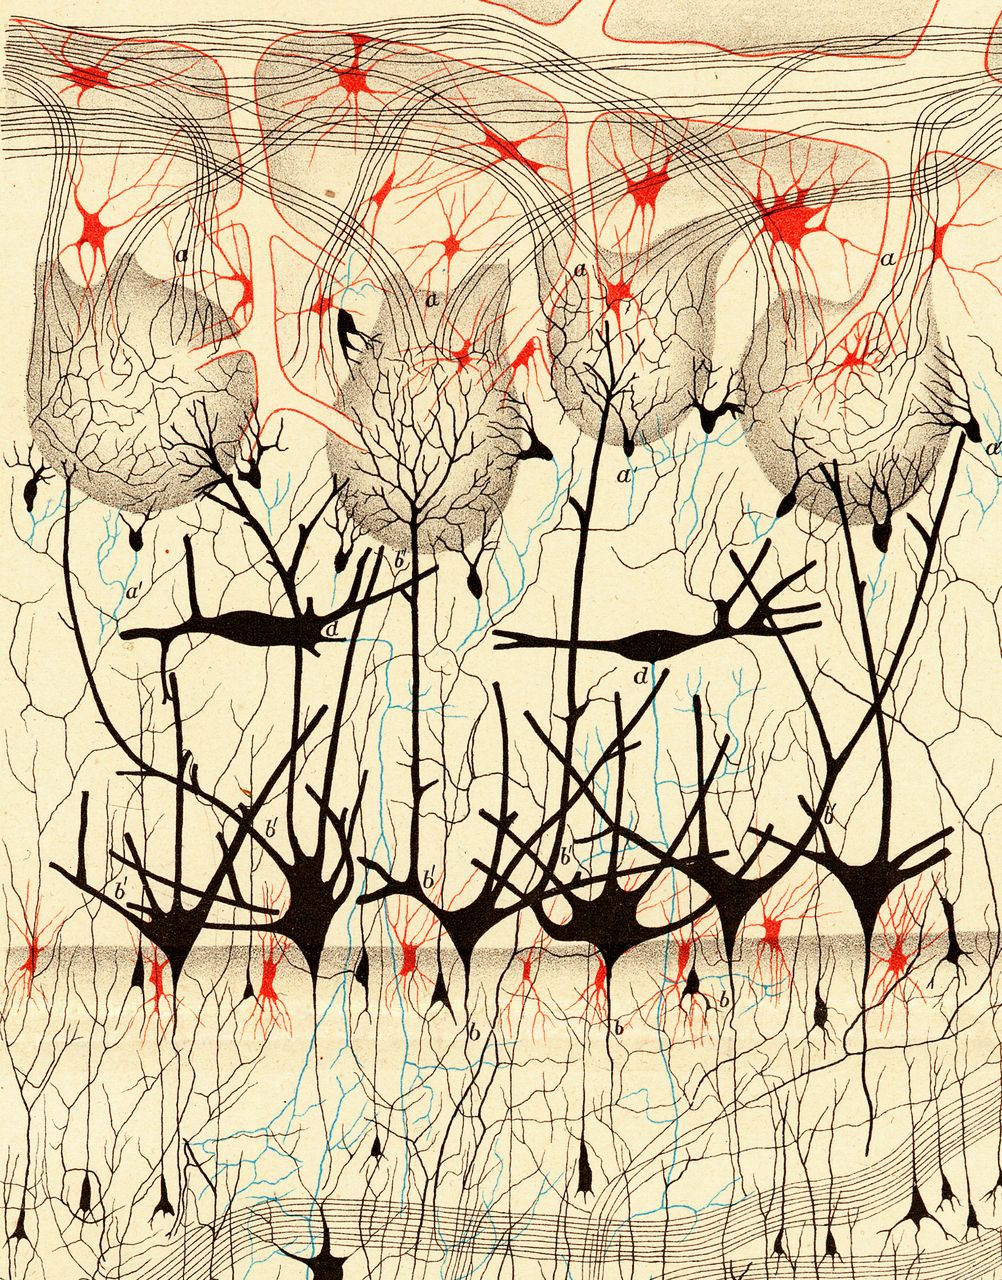
Enabling Researchers is a Moral Imperative (yorba.co)
What's wrong with AI? (homepage.farm)
This week's "node2shell" Brotli vulnerability (CVE-2026-111497) is exploitable in Python, other consumers of Brotli (www.aikido.dev)
Be Aware of What's in Your Logs (fireborn.mataroa.blog)
Wild version 0.11.0 released (github.com)
I want my Wednesday back (blog.luitjes.it)
Listening to Nina Simone in 2036 (punkx.org)
Big Runtimes Make Efficient Programs (www.youtube.com)
Twelve years of distributed SQLite (philipotoole.com)
Indian government sites are serving revoked eMudhra certificates (captnemo.in)
An Incremental Approach to JIT Construction (dl.acm.org)
Incremental Computation Graphs (dziban.net)
Memory is slow, Disk is fast (www.bitflux.ai)
Attention people who think UB is fine (blog.habets.se)
Distributed data, centralized fixes (miren.dev)
Railway Preliminary Report: Oct 21st Security Incident (blog.railway.com)

Getting Banned from r/java (sjhannah.com)

Next-Concept Modeling: Fast, Parallel Coarse-to-Fine Text Generation (arxiv.org)
A whirlwind tour of systemd-nspawn containers (2025) (quantum5.ca)
No Source Code? No Problem! What if you have to port a program, but all you have is a binary? (2003) (queue.acm.org)
Profiling Org-HTML formal grammar and optimizing it: orgwebalchemy (jointhefreeworld.org)
How to Make Things, and Why (www.youtube.com)
Release OpenSSL 4.1.0 · openssl/openssl (github.com)
AI-discovered bugs may soon trigger fresh disruptions, cyber experts say (www.reuters.com)
Emacs finally folds to my liking: kirigami, tree-sitter, hide-show, Org, XML (jointhefreeworld.org)
The glorious @xkcdRandom Zig builtin (ochagavia.nl)
a neat trick i found for reusing physical memory (sebsite.pw)
Software is slow because of bad design, not slow languages (www.seangoedecke.com)
How close can pure FP get to C? (rtfeldman.com)
What are you doing this weekend? (lobste.rs)

Debunking "Faster than Rust": Malicious Benchmarks in Tov (blog.fyralabs.com)

The Many Many Missed Opportunities of Sonic 06 (isaacmarovitz.com)
The Hibernate Origin Story (Outsider Edition) (fishbowl.pastiche.org)
UUIDv7 doesn't have the properties you think it does (alexsci.com)
Please don't mess with links (maurycyz.com)
Reliable Radio Communications using run-length limited Golaycodes (github.com)
We have Traits at Home (www.axelmagn.com)
a hacky fucked up way to portably access errno from outside of c (sebsite.pw)
Docker is weird (codeandcake.dev)
What is you opinion on submission quality since the vibecoding tag was removed? (lobste.rs)
Quad9 DNS Resolver to exit France (quad9.net)
Mojo v1.2.0 (mojolang.org)
Objects, attributes, maps, oh my (bernsteinbear.com)
Expose only share links of a private service with caddy (dataswamp.org)

Header Accordions: QPACK amplification attacks against HTTP/3 servers (foxio.io)
I built a garbage collector for Rust (2023) (claytonwramsey.com)
eMudhra to Exit global SSL/TLS Certificate Business (emudhra.com)
Script dependencies with Nix (entropicthoughts.com)
Tell your network to explain itself and then some (unixdigest.com)
The bridge to agent-scale Git infrastructure (github.blog)
jailbreaking the switch 2 (pepsipu.com)
There isn't an easy exploit for this PHP vulnerability (eliastaylor.com)

Create a Canarytoken. Deploy it somewhere (canarytokens.org)
Three configurable prettyprinters (2023) (reasonableapproximation.net)
Two Welsh organisations reprimanded after cyber-attack exposed children’s information (ico.org.uk)
Extending concurrent separation logic to the hardware level to verify the xv6 OS kernel on RISC-V with AI agents (arxiv.org)
Garmin Revamps and Opens Up Connect Developer API Program (www.dcrainmaker.com)
examining the macOS gcc binary (zoey-on-github.github.io)
Announcing DuckDB 2.0.0 LTS “Cinnamon Teal” (duckdb.org)